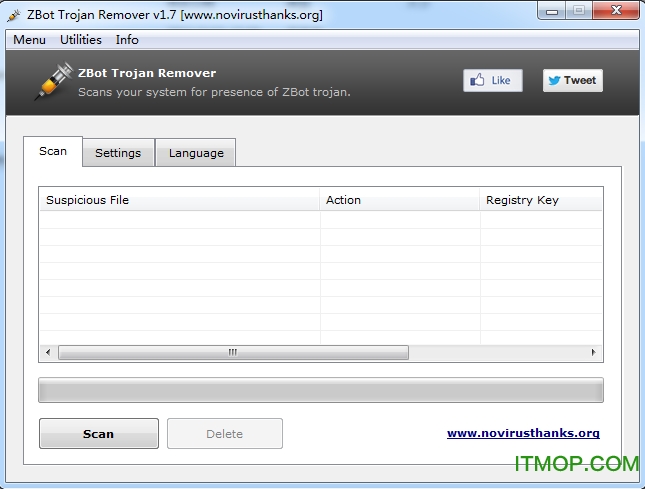
ZBot病毒查杀工具(ZBot Trojan Remover)
v1.7 绿色版 发表评论
- 游戏类别:病毒防治
- 游戏大小:554.00 KB
- 更新时间:2017-07-17 17:47
- 游戏版本:v1.7 绿色版
- 游戏语言:中文
- 游戏等级:
- 官方网址:暂无
评分:
好评:1
差评:0
游戏介绍
ZBot病毒查杀工具(ZBot Trojan Remover)是一款好用的病毒查杀软件,可以检测并查杀ZBot变种木马病毒,这病毒可以从网站上窃取用户的银行信息,信用卡信息和paypal账户的登录凭据。欢迎来IT猫扑网下载!
病毒样本:
Malware Analyzer by HX
Analysis started
MD5: 2BB9A1C4B35719ABD022C605A546D6C4
Executing -> DeviceHarddiskVolume3UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe (PID: 13440)
Command-line: &C:UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe&
C:UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe
WriteFile, C:UsersGatewayAppDataRoamingGolaxyeq.exe
C:UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe
WriteRegistryKey, SoftwareMicrosoft
C:UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe
WriteRegistryKey, Juat
C:UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe
DeleteFile, C:UsersGatewayAppDataRoamingGolaxyeq.exe
C:UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe
WriteFile, C:UsersGatewayAppDataRoamingGolaxyeq.exe
C:UsersGatewayDesktop2BB9A1C4B35719ABD022C605A546D6C4.exe
WriteFile, C:UsersGatewayAppDataRoamingGolaxyeq.exe
Executing -> DeviceHarddiskVolume3SandboxGatewayAnalyzerusercurrentAppDataRoamingGolaxyeq.exe (PID: 16540)
Command-line: &C:UsersGatewayAppDataRoamingGolaxyeq.exe&
C:UsersGatewayAppDataRoamingGolaxyeq.exe
WriteRegistryKey, SoftwareMicrosoftJuat
C:UsersGatewayAppDataRoamingGolaxyeq.exe
WriteRegistryKey, f62bfi
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
accessPROTECTEDProgram, C:WindowsSystem32taskhost.exe (PID: 1992)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:WindowsSystem32dwm.exe (PID: 2976)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:UsersGatewayAppDataLocalMicrosoftSkyDriveSkyDrive.exe (PID: 3484)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program Files (x86)GoogleDrivegoogledrivesync.exe (PID: 3496)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program FilessandboxieSbieCtrl.exe (PID: 3524)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program Files (x86)EvernoteEvernoteEvernoteClipper.exe (PID: 3584)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, K:Program Files (x86)Kaspersky LabKaspersky Endpoint Security 8 for Windowsavp.exe (PID: 3592)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:UsersGatewayDesktopgoagent-goagent-a51d6a2localgoagent.exe (PID: 3600)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:WindowsSystem32conhost.exe (PID: 3608)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program FilesBOINCboincmgr.exe (PID: 3696)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:UsersGatewayDesktopgoagent-goagent-a51d6a2localpython27.exe (PID: 3704)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program FilesBOINCboinctray.exe (PID: 3776)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, K:SkyDriveProgramsvbSherloggerSherlogger.exe (PID: 3840)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, K:Program Files (x86)BaiduYunbaiduyun.exe (PID: 3868)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program Files (x86)GoogleDrivegoogledrivesync.exe (PID: 3952)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program FilesBOINCboinc.exe (PID: 3964)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:WindowsSystem32conhost.exe (PID: 3972)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:Program Files (x86)alipaySafeTransactionAlipaySafeTran.exe (PID: 17800)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:ProgramDataBOINCprojectswww.worldcommunitygrid.orgwcgrid_dsfl_vina_6.25_windows_x86_64 (PID: 57092)
C:UsersGatewayAppDataRoamingGolaxyeq.exe (PID: 16540)
AccessPROTECTEDProgram, C:WindowsSystem32conhost.exe (PID: 58156)
Rolling back...
Analysis ended
Reason: Malware detected and rolled back
Anomalies:
- Modifies protected resource. The executable modifies important resources (files, processes, etc.)
下载地址
Pc版ZBot病毒查杀工具(ZBot Trojan Remover) v1.7 绿色版
本类推荐
 百度杀毒
 ClamAV杀毒软件
 瑞星CPU漏洞检测修复工具
 百度安全卫士电脑版
 360杀毒64位极速版
 金山毒霸电脑版
 卡巴斯基免费版(Kaspersky Free)
 小红伞个人免费版(Avira Free Antivirus)
 360安全卫士
 usbcleaner(u盘病毒专杀工具)
本类最新
 鸿合系统管家v1.0.0.20230821 官方版
 Hitman Pro反间谍杀毒工具v3.8.44.340 免费版
 文件夹病毒专杀工具v2.31 免费版
 LMT Anti Logger(系统防护软件)v4.6 官方版
 EX杀毒软件v3.0.1 官方版
 河马webshell查杀工具v1.8.2 官方版
 可牛杀毒u盘专杀工具v1.1 免费版
 ramnit病毒专杀工具v2.4.4.3 绿色版
 CyberLock(电脑杀毒软件)v7.88 官方版
 暗组Web杀毒v2.7 绿色版
 智量终端安全软件v3.07 官方版
 ESET Endpoint Antivirus32位/64位企业版标准防护版v13.1.2036.0 官方版
 ESET Endpoint Security电脑端官方正版v12.0.2058.0 简体中文版
 360cad病毒专杀工具(cadviruskiller.exe)v1.01 绿色免费版
 USB Disk Security(USB安全软件)v6.9.0 官方版
相关游戏
 天诺时空卡巴斯基2014激活工具永久授权版
kis2014激活工具是一款可以将卡巴斯基2014安全软件进行完美破解的工具,让用户可以免费永久使用这款软件防护电脑的安全.有需要的朋友就来IT猫扑下载吧!卡巴斯基2014激活工具使用方法第一步:删除卡巴斯基2014的授权,一定
 Cerbero Suite Advanced(恶意软件分析工具)v5.2.0 官方版
CerberoSuiteAdvanced最新版是一款专业的恶意程序分析查找工具,它可以自动查找分析电脑中恶意程序或者文件,对文件进行反编译,查找到恶意程序之后将这些城西分类出来;支持多种文件格式,可执行文件、文档、数据库、档案、字
 Dr.Web大蜘蛛密钥文件key激活码永久免费版
大蜘蛛key是一款可以针对Dr.Web大蜘蛛杀毒软件进行激活授权的文件,让用户们可以免费永久使用这款超级强大的杀毒工具,时时刻刻防护你的电脑安全.有需要的朋友就来IT猫扑下载吧!大蜘蛛杀毒软件介绍Dr.WEB就是被大家称
 incaseformat蠕虫病毒查杀工具v1.1.0.7 32位/64位版
incaseformat蠕虫病毒查杀工具是针对最近incaseformat病毒而开发的专杀工具,小编根据用户电脑的不同特地分享了32位和64位的系统,让您的电脑也能够受到保护,软件操作十分的简单,感兴趣的朋友可千万别错过了哦。病毒介绍该
下载排行
- 1360安全卫士13

病毒防治 / 3.90 MB - 2360安全卫士标准版
病毒防治 / 5.69 MB - 3360安全卫士精简版
病毒防治 / 34.13 MB - 4360安全卫士离线完整版
病毒防治 / 104 MB - 5Toolwiz Care(新加坡兔卫士)

病毒防治 / 7.10 MB - 6360安全卫士9.7
病毒防治 / 60.57 MB - 7360安全卫士经典怀旧版
病毒防治 / 82.00 MB - 8卡巴斯基(Kaspersky Anti-Virus)(附2009-12-23Key)
病毒防治 / 30.00 MB - 9瑞星杀毒软件最新版

病毒防治 / 46.3 MB - 10360安全卫士2014
病毒防治 / 60.57 MB


网友评论
查看所有0条评论